5Z CONSULTING PRODUCT SECURITY
Keep your connected products secure, CRA-compliant and sellable in Europe.
The Cyber Resilience Act turns product cybersecurity into an ongoing manufacturer responsibility. We help industrial companies build and operate vulnerability management, SBOMs, security updates, incident reporting and product-security evidence.

Hardware / Firmware / Software / Cloud
CRA Readiness · PSIRT-as-a-Service · SBOM Management · Vulnerability Operations · Incident Reporting
CRA reporting obligations begin 11 September 2026
Full CRA application: 11 December 2027
01 / THE OPERATING CHALLENGE
CE, EMC, machinery and electrical compliance have largely been managed around product launch. Product cybersecurity is different. Connected products need security support after sale.
Design → Release → Monitor → Detect → Remediate → Update → Report → Evidence
Manufacturers may need to identify software components, maintain vulnerability-handling processes, support security updates, respond to reports and maintain evidence throughout the product support period. The challenge is not simply understanding the regulation. It is operating the process continuously across an entire product portfolio.
CRA creates a new operating function inside many traditional manufacturers.
Build internally
Product Security Manager
Vulnerability / Security Engineer
Compliance specialist
PSIRT capability
SBOM tooling
Vulnerability monitoring
External testing
Incident-response procedures
Regulatory monitoring
For many mid-market manufacturers, this means several specialist roles plus tooling and external expertise.
5Z Consulting
Specialist product-security capability
Defined CRA operating processes
Portfolio-wide vulnerability management
PSIRT capability
SBOM operations
Incident-reporting support
Technical evidence
Continuous regulatory monitoring
Add the capability without building the entire function internally.
02 / PRODUCT SECURITY OPERATIONS
We don’t just tell manufacturers how to comply. We help operate the process.
01
CRA Readiness & Implementation
Determine scope, classify products, assess gaps and create the implementation roadmap required for CRA readiness.
02
PSIRT-as-a-Service
Operate vulnerability intake, triage, coordination, advisories and escalation as the manufacturer’s Product Security Incident Response capability.
03
SBOM & Component Security
Build and maintain visibility over software components, dependencies and known vulnerabilities across product families.
04
Vulnerability Operations
Continuously monitor, assess, prioritise and track vulnerabilities affecting shipped products.
05
Incident Reporting
Create processes and evidence to support CRA Article 14 reporting and the 24/72-hour notification workflow.
06
Product Security Evidence
Maintain risk assessments, security documentation, remediation evidence, support-period records and conformity-related technical documentation.
See how Managed Product Security works
5Z supports CRA readiness, implementation and ongoing product-security operations. Where independent testing, certification or conformity assessment is required, this must be performed by the relevant authorised third party.
03 / A CLEAR STARTING POINT · 2–4 WEEKS
A fixed-scope assessment of your connected-product portfolio designed to establish what CRA requires, where the major gaps are and what should happen next.
Typical engagement: 2–4 weeks. Fixed-scope engagements available for mid-market manufacturers.
01
Product Scope
Identify products and product families likely to fall within CRA scope.
02
Classification
Map relevant product categories and likely conformity routes.
03
Product Security Maturity
Assess product-security maturity, vulnerability-management readiness and secure-development gaps across development, updates and documentation.
04
SBOM Readiness
Determine whether components and dependencies can be reliably identified and maintained.
05
PSIRT Readiness
Assess intake, triage, escalation, disclosure and remediation capability.
06
Article 14 Reporting Readiness
Evaluate identification and escalation of potentially reportable vulnerabilities and severe incidents within required timelines.
07
Support-Period Obligations
Assess long-term security support and updates across installed products.
08
Implementation Roadmap
Prioritised implementation roadmap with ownership, dependencies and a build-vs-outsource recommendation.
CRA Portfolio Readiness
ILLUSTRATIVE EXAMPLE
Product inventory & scope: 72%
Governance & ownership: 58%
Secure development: 56%
SBOM & component security: 34%
Vulnerability handling: 42%
PSIRT & Article 14: 28%
Security updates & support: 47%
Technical evidence: 55%
38 product families
Eight readiness domains
12-month roadmap
Selected pages
SELECTED EXCERPT
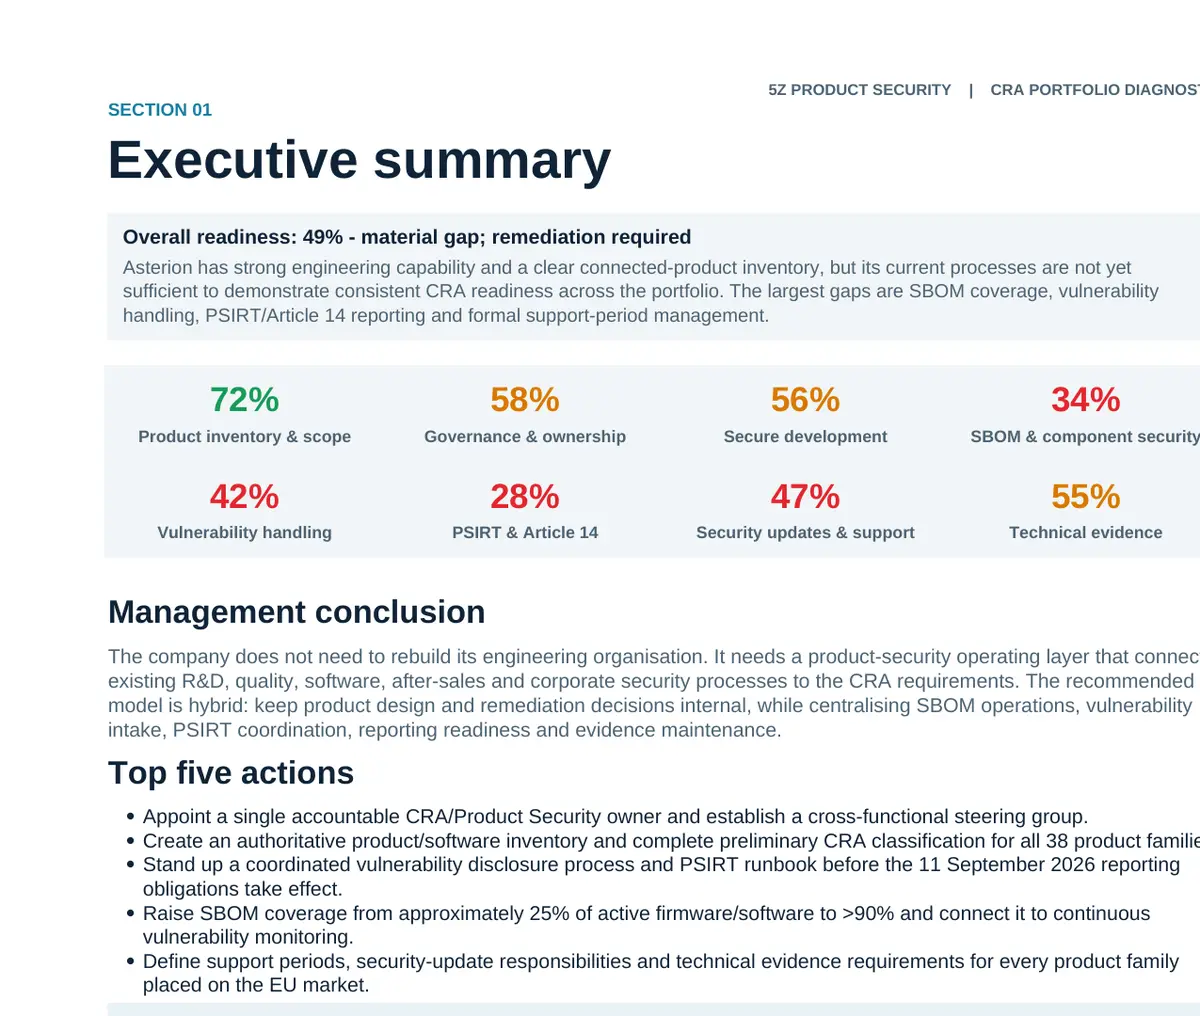
Preview excerpt · remaining content omitted
SELECTED EXCERPT
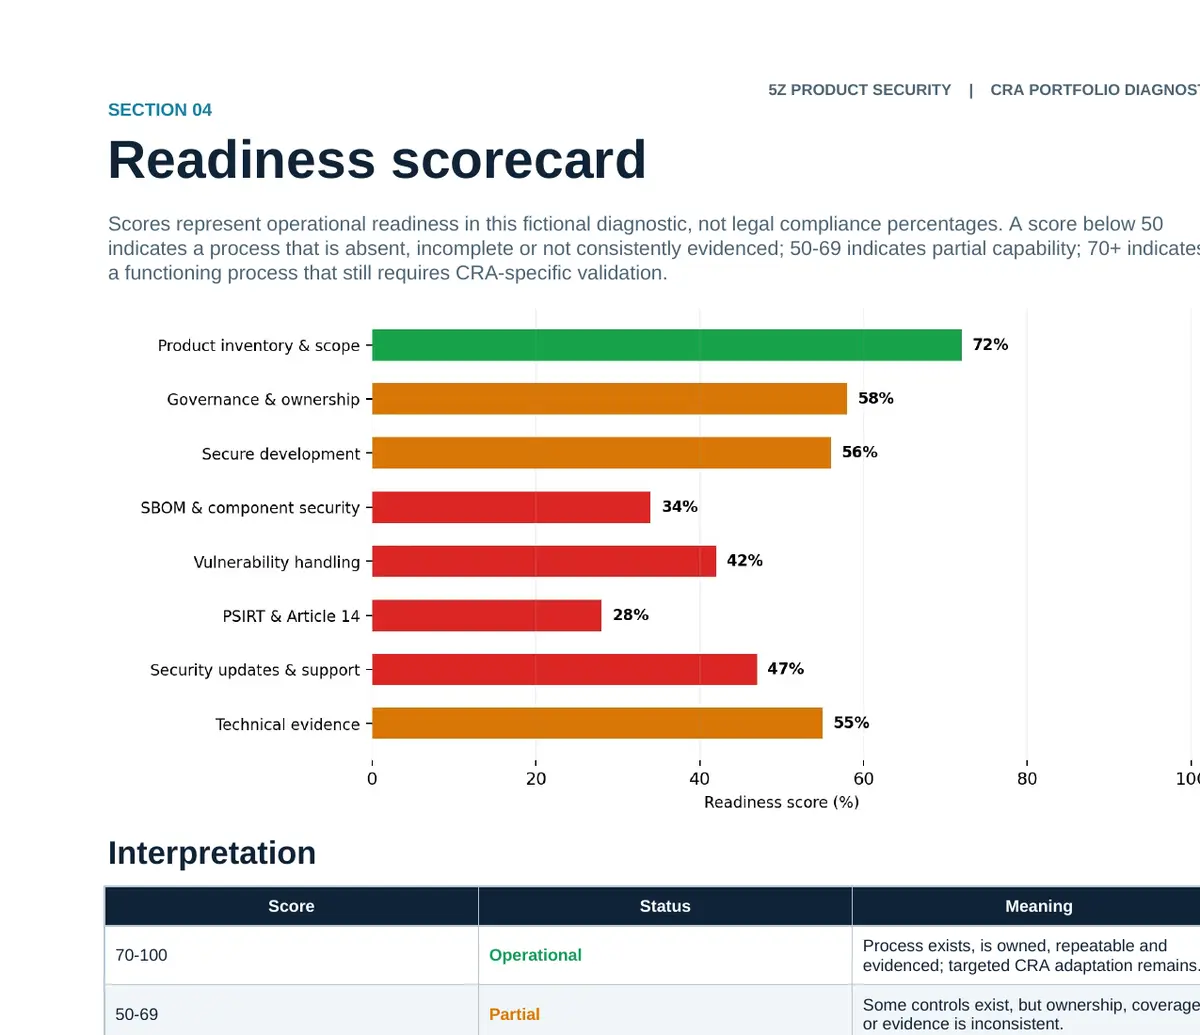
Preview excerpt · remaining content omitted
SELECTED EXCERPT
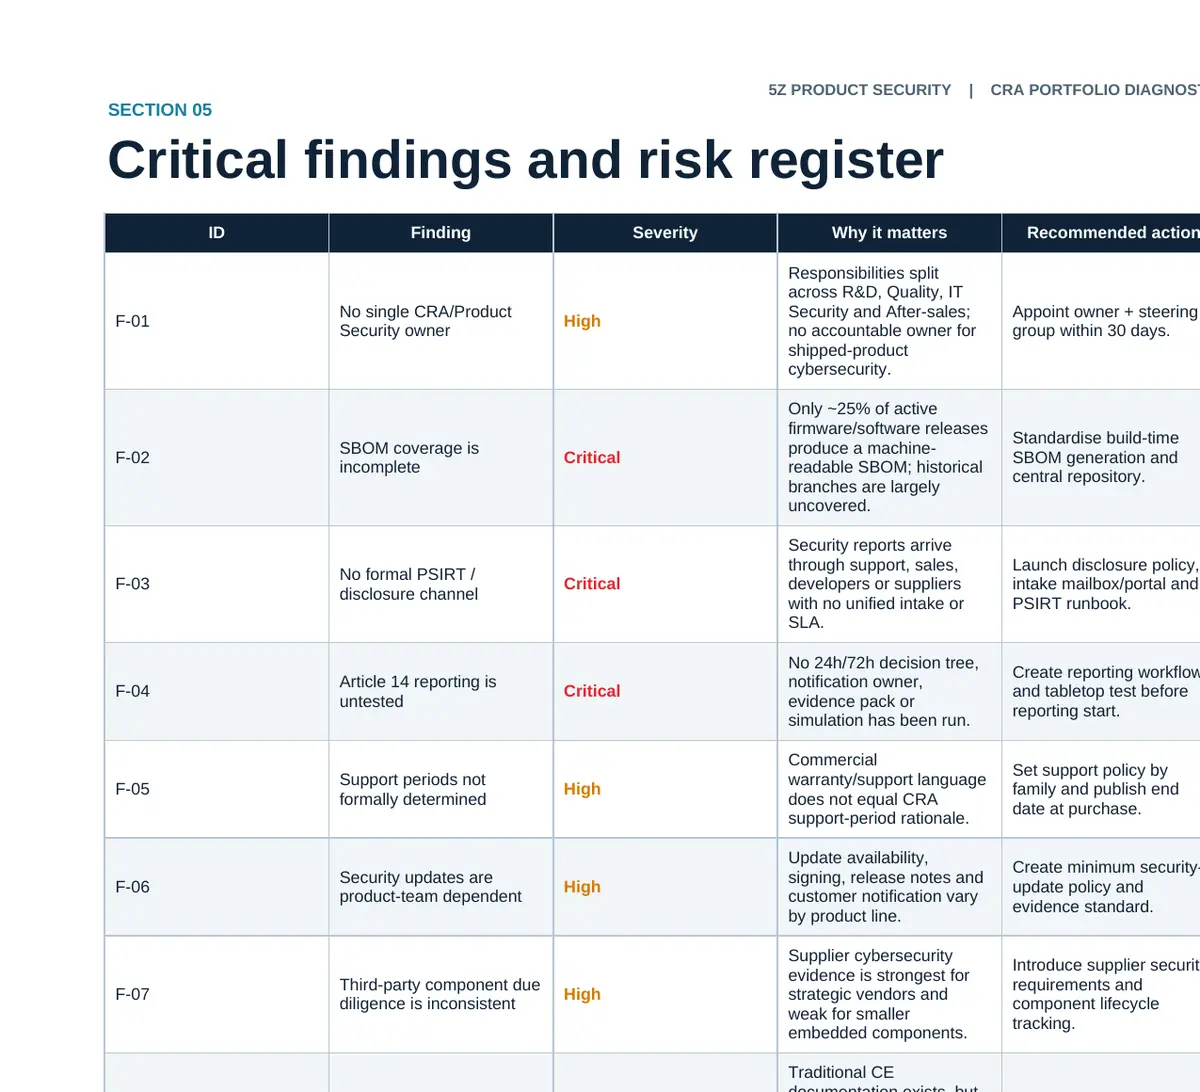
Preview excerpt · remaining content omitted
SELECTED EXCERPT
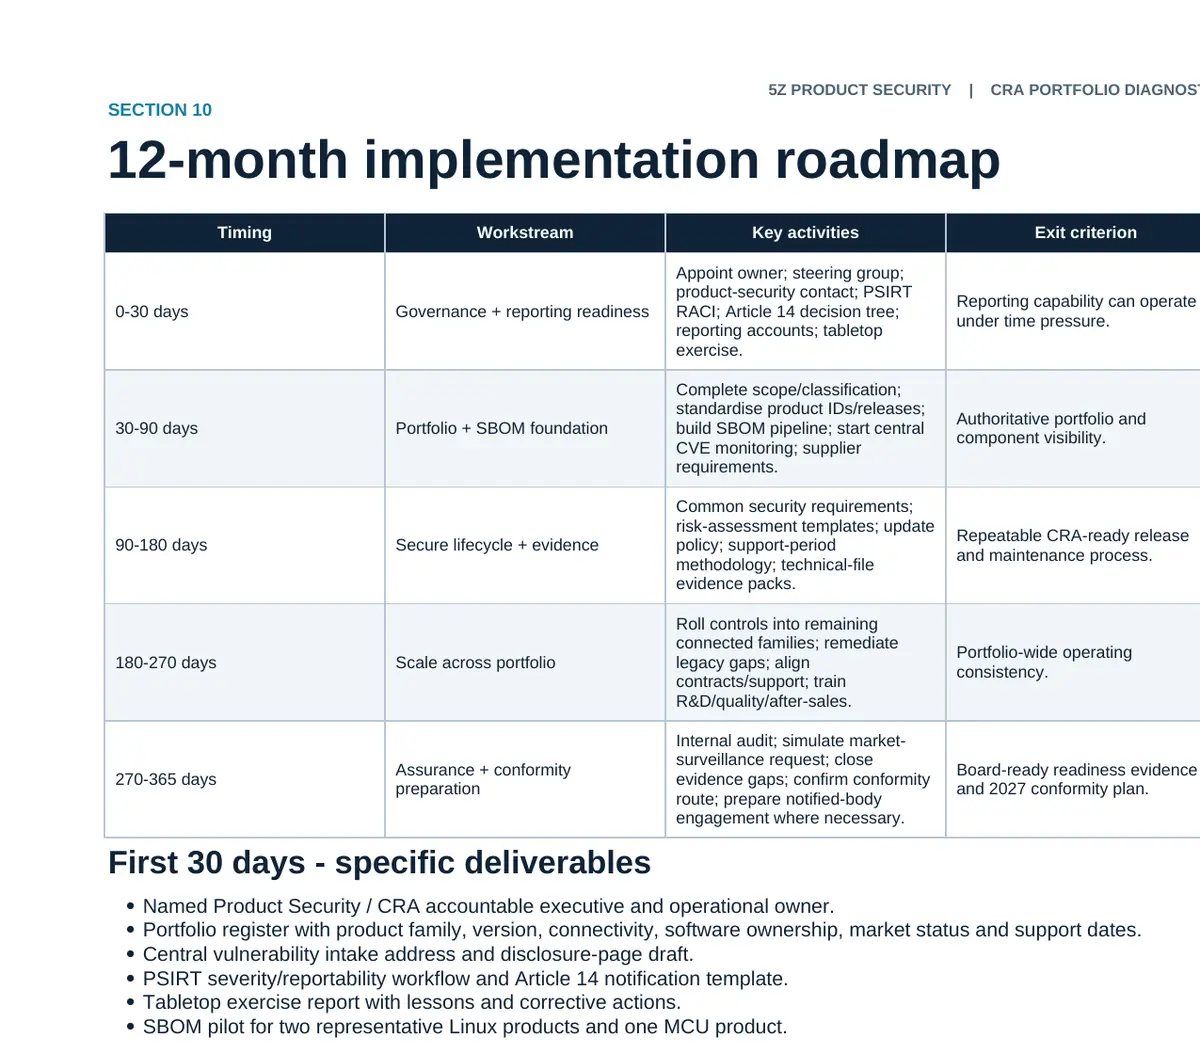
Preview excerpt · remaining content omitted
04 / INDUSTRIAL BY DESIGN
For engineering products that now include software, firmware, connectivity, remote services or cloud functionality.
01
Industrial Automation
02
HVAC & Refrigeration
03
Machine Tools
04
Packaging Machinery
05
Electrical Equipment
06
Pumps & Water Systems
07
Building Controls
08
Access & Security Systems
Our ideal customer is not a software startup.
It is a manufacturer that has spent decades building excellent physical products and now finds that those products contain software, network interfaces and long-term cybersecurity obligations.
Designed for manufacturers with connected products
Typically €30m–€300m revenue, 100–1,500 employees and multiple connected product families, with established R&D and quality teams but limited dedicated product-security resources. This includes industrial electronics and the sectors above; these are indicators of fit, not strict eligibility requirements.
01
Discover
Map products, software components, interfaces, support periods and current security processes.
02
Implement
Establish governance, SBOM, vulnerability, disclosure, reporting and evidence processes.
03
Operate
Run vulnerability intake, triage, monitoring, remediation tracking and reporting continuously.
04
Evidence
Maintain the technical and regulatory record needed to demonstrate that obligations are being managed.
We don’t just tell manufacturers how to comply. We help operate the process.
Product architecture. Firmware information. SBOM data. Vulnerabilities. Engineering documentation. Source-code access. Support information. These are sensitive engineering assets, not ordinary project files.
NDA available before technical information is exchanged
Least-privilege access
Customer-controlled repositories where appropriate
Encrypted data transfer and storage
EU-based hosting where practical
Clear data-retention controls
Controlled access to vulnerability information
No customer information used to train public AI models
Customer approval before sensitive material is shared with third parties
Our security architecture and information-handling procedures are available for review during procurement.
01
Product, not corporate IT
We focus on the cybersecurity lifecycle of products placed on the market, rather than general corporate cybersecurity.
02
Operations, not just advice
We help operate recurring vulnerability, PSIRT, SBOM and evidence processes after the initial assessment.
03
Built for the mid-market
For manufacturers that need specialist capability without building a large permanent internal team.
5Z Product Security is focused specifically on the operational requirements created by the Cyber Resilience Act and modern connected-product regulation.
Focused specifically on product security
5Z Product Security is not a general managed-IT or corporate cybersecurity provider. We focus on the security lifecycle of products placed on the market: embedded software, firmware, product interfaces, software components, vulnerability handling, security updates, support periods, PSIRT, technical evidence and product incident reporting.
01
10 December 2024
CRA entered into force.
02
11 September 2026
Article 14 vulnerability and severe-incident reporting obligations begin.
03
11 December 2027
Main CRA requirements become fully applicable.
Product inventories, SBOM processes, vulnerability management, secure-development evidence and PSIRT capability should be in place well before full application.
Discuss your readiness
Product cybersecurity requirements are becoming more important across major markets. A common product-security operating layer helps manufacturers manage European CRA obligations while preparing for other frameworks and market-access requirements. Support is scoped to the applicable products, markets and obligations.
EU CRA · IEC 62443 · UK product-security requirements · US product-security frameworks · Global vulnerability management
Requirements and conformity routes remain specific to each framework and jurisdiction. One assessment does not automatically satisfy another market’s requirements.
CRA compliance sits at the intersection of cybersecurity, embedded software, engineering, product lifecycle management and conformity obligations.
Product Cybersecurity
Vulnerability management, SBOMs, secure development, software components, updates and incident response.
CRA & Product Compliance
Product scope, classification, regulatory obligations, technical evidence, support periods and conformity readiness.
Industrial Engineering Context
Product security must work within real manufacturing environments, long product lifecycles, field-service processes and existing R&D workflows.
Where specialised testing or independent conformity assessment is required, 5Z works alongside appropriate laboratories, testing providers and conformity-assessment organisations.
A short initial discussion can determine whether your organisation needs a full CRA programme, targeted remediation or an outsourced product-security operating function.
Confidential discussion. NDA available.